



You run crews across several California job sites, buddy punching is costing real money, and a face recognition time clock would fix it. Then someone asks whether it is legal. The short answer under California biometric privacy law is yes, with conditions. The longer answer changed in 2026, and it changes again on January 1, 2027.
This guide is for HR, operations, and compliance leads at companies managing hourly and multi-site workforces in California. It covers what the law governs, who it applies to, the obligations that attach to each step of a rollout, the three new laws that take effect in 2027, and what to look for in a system built to meet them.
Does California have a biometric privacy law?
Not a standalone one. If you searched for a California Biometric Information Privacy Act expecting an Illinois-style statute, it does not exist. California regulates biometric data inside its general privacy law, the California Consumer Privacy Act, enacted in 2018 and operative from January 1, 2020. The California Privacy Rights Act, passed as Proposition 24 in November 2020, amended and expanded it rather than creating a separate law. The state's privacy regulator, the California Privacy Protection Agency, refers to the combined framework as the CCPA.
Under the CCPA, biometric information means physiological, biological, or behavioral characteristics that can be used to establish identity. A photograph on its own is not biometric data. The moment it is processed into a faceprint for recognition, it is. Biometric data used to identify a person is also sensitive personal information, which carries a higher set of obligations than a name or an email address.
Two facts decide whether California biometric privacy law applies to you:
- Employees are covered. The employment exemption expired on December 31, 2022. Since January 1, 2023, W2 employees, 1099 contractors, and hourly workers who are California residents hold the same data rights as consumers.
- Thresholds decide coverage. The CCPA applies to a for-profit business that does business in California and meets any one of three tests: annual gross revenue above $26,625,000 (the figure through 2026; the CPPA adjusts it for inflation in odd-numbered years, with the next adjustment on January 1, 2027), buying, selling, or sharing the personal information of 100,000 or more California residents or households a year, or earning half or more of its revenue from selling or sharing personal information.
A facility management company running cleaning crews across 40 client buildings in California will usually clear the revenue test. A regional contractor may not. Below the thresholds, the CCPA does not apply directly, but the Labor Code provisions covered later apply to every employer, and following the CCPA framework anyway is the cheapest way to keep a biometric rollout defensible.
The practical difference for a contractor enrolling crews in face attendance: California does not require a signed consent form from each worker before enrollment the way Illinois does. It requires notice before collection, a documented purpose, and the ability to honor data rights. That is a lighter front door, not lighter oversight. The CPPA can audit and fine on its own initiative, without a complaint or a breach.
Is facial recognition legal in California for private employers?
Yes. No California statute bans a private employer from using face recognition to verify who is clocking in. The restrictions that make headlines apply to government use, and the new workplace law signed in 2026 is narrower than the early coverage suggested.
AB 1883 adds Labor Code sections 1580 to 1583, effective January 1, 2027. Earlier drafts would have limited facial recognition to unlocking devices and securing areas. The version signed on September 30, 2026 dropped that. The final text prohibits an employer from using an AI workplace surveillance tool on employees for two things: recognizing or inferring an individual's emotional state, and collecting neural data. A face match that answers one question, is this the enrolled worker, does neither.
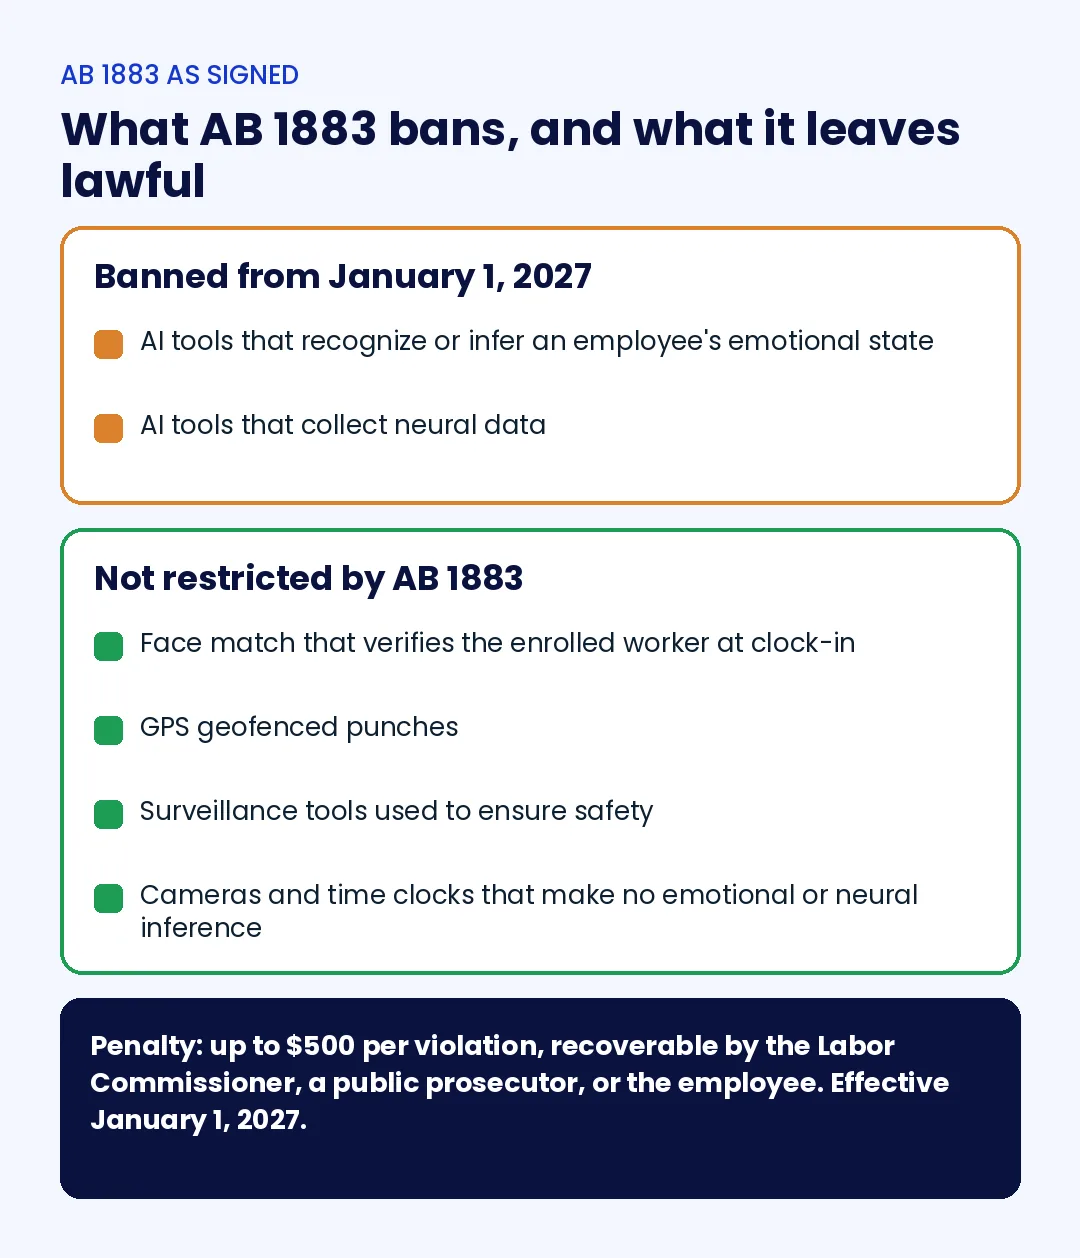
Three details in the final text matter for a multi-site employer. First, the definition of a workplace surveillance tool is broad enough to include a biometric time clock, so the law applies to the tool; it simply does not prohibit identity verification. Second, employer includes labor contractors and the client employers that use them, so a staffing arrangement does not move the duty elsewhere. Third, the penalty is up to $500 per violation, recoverable by the Labor Commissioner, a public prosecutor, or the employee, which is the first direct employee recovery right attached to workplace biometrics in California.
The operational rule that follows is simple. Use face recognition to verify identity. Do not switch on any feature that reads mood, attention, stress, or engagement from a worker's face, and do not buy a system that cannot keep those functions off.
What changed in California biometric privacy law in 2026 and 2027
The CCPA itself did not change its treatment of biometrics. What changed is the regulations under it and three new Labor Code laws. Together they turn California biometric privacy law from a notice-and-rights regime into one with documentation, audit, and human-review duties.

The risk assessment is the change most employers have not heard about. The CPPA's regulations took effect on January 1, 2026 and treat processing sensitive personal information, and using biometrics to verify identity, as processing that presents a significant risk. A business in scope must complete a risk assessment before it starts, documenting purpose, categories of data, safeguards, and the benefits weighed against the risks. Processing that was already running on January 1, 2026 has to be assessed by December 31, 2027, and the first summary report goes to the agency by April 1, 2028. A construction company that enrolled its California crews in face attendance in 2024 is already inside that window.
What California biometric privacy law requires at each step of a rollout
Compliance is not a form signed once. Each obligation attaches to a specific moment in the clock-in workflow, which is why the system you choose decides how much of this your team has to do by hand.
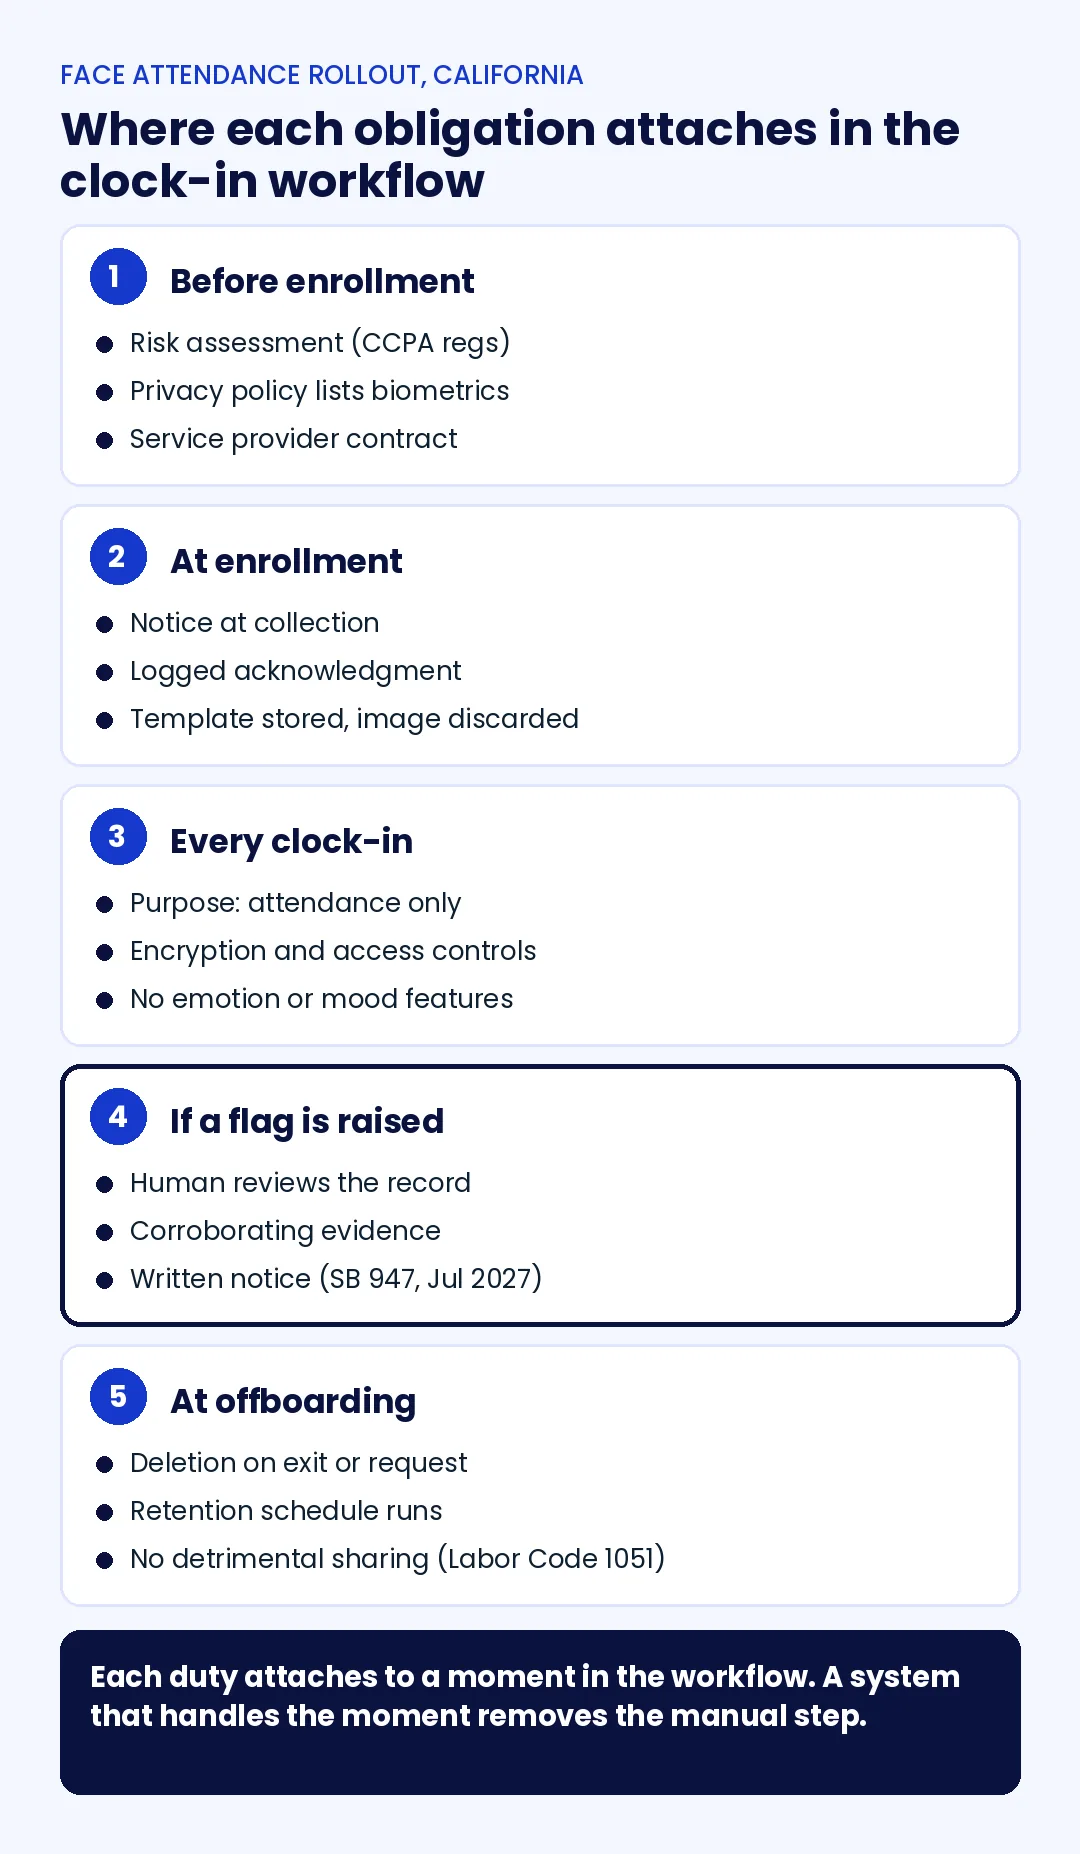
Before enrollment: risk assessment, privacy policy, vendor contract
Complete the risk assessment if the CCPA applies. Update the privacy policy so it lists biometric information as a category collected, the purpose, the retention period, and the vendor it is shared with. Put a service provider contract in place that limits the vendor to providing the attendance service, sets security and breach notification terms, and covers deletion at termination. A vendor that cannot sign those terms is not ready for California.
At enrollment: notice at collection
Every worker must be told what is being collected and why before the first facial scan. The notice has to reach W2 employees, agency workers, and 1099 contractors alike, and it has to be provable. A notice delivered inside the enrollment flow, with an acknowledgment logged against the worker's record, beats a paper form in a site trailer.
At every clock-in: purpose limitation and security
The stored template may be used for the disclosed purpose, verifying attendance, and nothing else. Reasonable security is required: encryption in transit and at rest, access controls, and a retention policy. A breach of unencrypted biometric data caused by inadequate security gives affected workers a private right to sue under the CCPA, with statutory damages of $100 to $750 per consumer per incident in the statute, adjusted upward for inflation by the CPPA.
When a worker asks: know, delete, limit
Workers can ask what biometric data was collected and how it is used, with a response due within 45 days. They can ask for deletion, subject to exceptions where the data is still needed for the employment relationship or a legal duty. The right to limit use of sensitive personal information applies when data is used beyond the purposes the law already permits; the regulations list using biometric information to verify identity as a permitted purpose in the employment context, so this right does not let a worker opt out of a face clock-in while still being paid for the shift. Treat a refusal as an HR conversation, not a data-rights request.
When attendance data is used for discipline: human review
From July 1, 2027, SB 947 bars relying solely on an automated decision system to discipline or fire a worker. If the system's output is the main basis, a human has to review it and corroborate it with other evidence, and the worker gets written notice. An attendance anomaly flag, such as a pattern of late punches across three sites, is a prompt for a supervisor to check the record, not a verdict. Our guide to how to detect time theft across multiple job sites covers how flags of that kind should be handled.
At offboarding: deletion and retention
When a worker leaves, the biometric template should be deletable, and the retention schedule you disclosed should actually run. California Labor Code section 1051 adds a separate rule that applies regardless of the CCPA thresholds: an employer may not share an employee's fingerprints or photographs with a third party where they could be used to the employee's detriment.
What non-compliance costs
The exposure scales with headcount, which is what makes it different from most compliance line items.
- CPPA administrative fines: up to $2,663 per unintentional violation and $7,988 per intentional violation, assessed per affected individual. A non-compliant rollout across 300 California workers is 300 potential violations, not one.
- Breach lawsuits: statutory damages per worker per incident for unencrypted biometric data exposed through inadequate security, with class actions allowed.
- AB 1883 penalties from 2027: up to $500 per violation, recoverable by the employee directly.
- SB 947 from July 2027: Labor Commissioner enforcement where discipline or termination rested on an automated output without human corroboration.
A general contractor with 300 workers across six California sites who skipped the notice step is looking at a worst case near $800,000 in unintentional-violation fines before anyone files a breach claim. Getting enrollment right costs a fraction of that.
What to look for in a California-compliant face recognition time tracking system
Most of the obligations above can be met by the system or left for your HR team to patch manually. The checklist below is the compliance half of the questions in our guide on how to choose a face recognition attendance system.
- Consent and notice inside enrollment. The notice appears before the camera opens, the worker acknowledges it, and the acknowledgment is logged.
- Templates, not photos. The system converts the scan to a mathematical template and discards the image.
- No emotion or attention features. Identity verification only, with no way for a site manager to enable inference features that AB 1883 bans.
- Deletion and retention controls. Individual templates can be removed, and retention schedules are configurable per the policy you disclosed.
- Audit logs. Every enrollment, clock-in, and data request is logged with a timestamp, so a risk assessment and a CPPA inquiry can both be answered from the record.
- Role-based access. Biometric records are visible only to the people who need them.
- Service provider terms and certifications. A CCPA-compliant data processing agreement, plus ISO 27001 and SOC 2 as evidence the controls were audited.
- Offline capture with secure sync. Remote sites with no signal still produce a verified, encrypted record.
- Flags, not verdicts. Any AI feature that spots attendance anomalies should present them for human review, which is what SB 947 will require.
Companies managing contract and field crews across several California locations feel every item on this list at once, because turnover is high, sites change, and the same worker may be enrolled by an agency one month and directly the next.
How Truein supports California biometric privacy compliance
Truein is a face recognition and GPS-based time and attendance platform for contract and multi-site workforces, used by 500+ customers across 10,000+ locations. It is built for the workforces this article describes: construction, facility management, property management, and contracting companies running W2, agency, and 1099 workers across California sites. One point to state upfront: Truein provides the controls. Whether a deployment is compliant depends on how your organization configures and runs them, and on the risk assessment and policies your team owns.
- Consent before collection. Workers see a consent screen in the Truein app and must tap to agree before the camera opens. The step is configurable by the admin and enforced across every site.
- No raw image storage. The enrollment scan becomes a mathematical template and the original image is discarded. Verification at clock-in runs against the template.
- Identity only. Truein's AI matches a face to an enrolled profile. It does not run generative AI, does not train models on customer data, and does not infer emotion, attention, or any other state.
- Your data stays yours. Truein processes attendance data as a service provider on your behalf and does not sell, share, or use it for any other purpose.
- Tested security. ISO 27001 and SOC 2 certified, encrypted at rest and in transit, with regular penetration testing and a dedicated Data Protection Officer and CISO.
- Deletion and retention. Templates and records can be removed when a worker leaves or a validated request arrives, with configurable retention schedules.
- Flags for human review. AI TimeGuard surfaces attendance anomalies for a supervisor to check against the record. It does not take disciplinary action.
- Built for the sites you run. No dedicated hardware, offline capture that syncs later, and separate agencies for subcontractor and staffing crews. The face recognition time clock for construction crews page covers the site setup.
Truein also aligns with GDPR and India's Digital Personal Data Protection Act, so the same privacy-by-design controls apply across markets rather than being bolted on for one state.
Conclusion
California does not ban face recognition time tracking. It regulates it, and from 2027 it regulates what you do with the data a little more. The CCPA sets the notice, data rights, security, and now risk assessment duties. AB 1883 bans emotion and neural inference, not identity verification. SB 947 puts a human between an attendance flag and a termination letter. For companies managing crews across multiple California sites, the operational case for face attendance is unchanged: verified clock-ins, no buddy punching, payroll built on records rather than recollection.
The compliance question is not whether you can use it under California biometric privacy law. You can. The question is whether your system delivers the notice, keeps only a template, logs everything, leaves inference features off, and lets a person make the decisions. Get that in place before go-live, and the law shapes the rollout instead of stopping it.
This article is general information, not legal advice. California privacy and employment laws change often and apply differently depending on your organization's structure, data practices, and workforce. Confirm your obligations with qualified counsel.
Frequently asked questions
Does California have a biometric information privacy act?
No. California has no standalone biometric statute. Biometric data is regulated as sensitive personal information under the CCPA, as amended by the CPRA, alongside Labor Code rules on employee photographs and fingerprints and, from 2027, the workplace surveillance and automated decision laws.
Does AB 1883 ban facial recognition at work in California?
It does not. The signed version of AB 1883, effective January 1, 2027, prohibits AI workplace surveillance tools from inferring an employee's emotional state or collecting neural data. Earlier drafts that limited facial recognition to unlocking devices were removed before passage. Using a face match to verify identity at clock-in remains lawful.
Can an employee refuse to use a biometric time clock in California?
California does not give workers a statutory opt-out from a face or fingerprint time clock used for attendance, because identity verification is a permitted use of sensitive personal information in the employment context. Workers do have rights to notice, access, and deletion. Employers should still handle refusals case by case, since disability, religious, and union obligations can apply.
Do I need a risk assessment before using face recognition for attendance in California?
If the CCPA applies to your business, yes. Since January 1, 2026, processing sensitive personal information and using biometrics to verify identity count as significant-risk processing that requires a documented risk assessment before it begins. Processing that was already running on that date must be assessed by December 31, 2027, with a summary reported to the CPPA by April 1, 2028.
What are the penalties for violating California biometric privacy rules?
Under California biometric privacy law, the CPPA can fine up to $2,663 per unintentional violation and $7,988 per intentional violation, counted per affected person. Workers can sue over breaches of unencrypted biometric data caused by inadequate security. From January 1, 2027, AB 1883 adds a penalty of up to $500 per violation that an employee can recover directly.
Does the CCPA cover 1099 contractors and agency workers, not just employees?
Yes. Since the employment exemption ended on December 31, 2022, every California resident whose data a covered business collects has the same rights, whatever their classification. AB 1883 and SB 947 go further and define employer to include labor contractors and the client employers that use them.
